I shipped a new feature on LaraPlugins.io this week: security advisories for Laravel packages. They check plugin versions against known vulnerabilities.
The very first thing they did? Surface a bug I had missed for two months.
What broke
A while back, I restructured the data sync pipeline. I disabled the old Packagist version sync commands and noted them in the code as "replaced." The replacement command, app:plugin:health-sync-all, did sync health scores. But it did not sync plugin versions.
Health scores, search, and everything else kept updating. So there was nothing visibly wrong. It was only when the new security advisory feature started cross-referencing version data that the stale state surfaced.
When advisories first launched, they compared plugin versions against our local data, which was stale. This is what tipped me off. Some plugins were showing lower Health scores than they should because the version information was behind.
What was fixed
I re-enabled the daily version sync (top 5,000 packages) and the weekly full sync (all packages). The two-month backlog was significant. I switched from loading all records into memory to using cursor-based iteration with chunk(), which cut peak memory usage substantially and lets the backlog process safely.
Version sync is now also explicitly part of the weekly health pipeline too.
For security advisories specifically, I added a fallback to the live Packagist API. Even if local version data is temporarily behind, advisory checks use the latest version info from Packagist directly. This means advisory badges stay accurate regardless of sync state. The gap was discovered because of the feature. The feature is now resilient to it.
While I was in the pipeline anyway
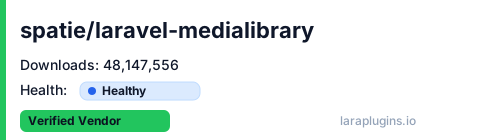
I also improved something I hope maintainers will find usefull: health badges for your README. They show your plugin's health score and security status at a glance.
[](https://laraplugins.io/plugins/vendor/package)Replace vendor/package with your Packagist package name or just use the get embed button on the plugin page on laraplugins.
The badge updates automatically with the new data on the site.
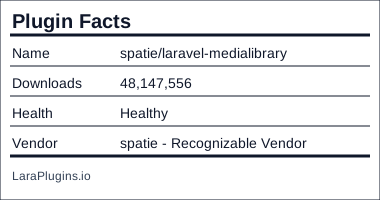
Here is an example of the generated badges using spatie/laravel-medialibrary as an example. The Plugin fact checks is my favorite.
If you use LaraPlugins to evaluate packages
Your data is current now. Security advisory scores are backed by live version data. You can also pull advisories directly in your editor via the LaraPlugins MCP server without visiting the site.
Timeline
The fix is deployed. The backlog of version data will take 4 to 8 hours to fully catch up. Everything should be current within the day.
Transparency is part of building in public. Sharing what went wrong, what I fixed, and what I learned, that is the whole point i think.